← Exams and Quizzes | Professional Exams →
Notice
If you get a question wrong, you can still click on the other answers. This will open up hints and explanations (if available), which will provide additional information. Exam should be 1 minute per question and please time accordingly.It is not required to have CompTIA A+ certification prior to obtaining CompTIA Network+ certification. It is recommended to have CompTIA A+ certification or the knowledge of the subject matter that is covered under A+ certification exam before taking Network+ certification exam. It is also recommended, but not required, that you have about 12 months of IT networking work experience.
Go to: Set I | Set III
CompTIA Network+ N10-007 - Set II
Congratulations - you have completed CompTIA Network+ N10-007 - Set II.
You scored %%SCORE%% out of %%TOTAL%%. With incorrect multiple attempts, your score is %%PERCENTAGE%%. Your performance has been rated as %%RATING%%
Question 1 |
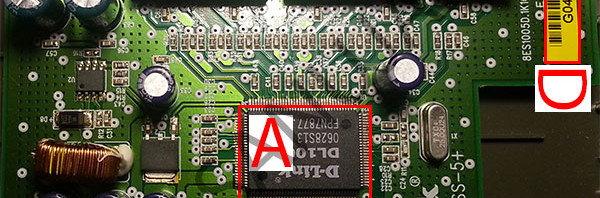
A | Fibre Channel |
B | RDMA |
C | PPP |
D | iSCSI |
Question 2 |
A | Attenuation |
B | Damaged cable |
C | Switch configuration |
D | Incorrect pin-out |
Question 3 |
A | Establish a theory of probable cause |
B | Duplicate the problem |
C | Test solutions |
D | Document findings |
E | Implement preventive measures |
F | Question users |
Question 4 |
“The Security certificate presented by this website was not trusted by trusted certificate authority.”
Sanuja has cleared his cache and cookies, rebooted his machine, and attempted to browse to the website from a coworker’s desktop, but it still presented with this error. Which of the following is the MOST likely cause of this error?
A | The SSL certificate has expired. |
B | The website is missing an HTTPS certificate. |
C | TLS is not enabled in the browser. |
D | The web server is missing an intermediate certificate. |
Question 5 |
A | GBIC |
B | RJ45 |
C | LC |
D | SFTP |
E | SC |
F | DB-9 |
Question 6 |
A | TCP/IP |
B | SQL |
C | DNS |
D | DHCP |
Question 7 |
A | Synchronization of clocks over a computer network |
B | Allocation of IP addresses |
C | Retrieving contents of an Internet page from a web server |
D | Monitoring of network-attached devices |
Question 8 |
A | Activate MAC address filtering. |
B | Disable the SSID broadcast. |
C | Implement WEP authentication. |
D | Change the WiFi password. |
Question 9 |
A | Disable unused ports. |
B | Upgrade the firmware. |
C | Reset the two-factor token. |
D | Disable virtual ports. |
Question 10 |
A | Reviewing a baseline report |
B | Reviewing application logs |
C | Reviewing SLA requirements |
D | Reviewing a vulnerability scan |
Question 11 |
A | Spam |
B | Ransomware |
C | Man-in-the-middle |
D | Phishing |
Question 12 |
A | Reverse the wires leading to pins 2 and 3 |
B | Reverse the wires leading to pins 1 and 2 |
C | Reverse the wires leading to pins 2 and 4 |
D | Reverse the wires leading to pins 1 and 3 |
Question 13 |
A | Duplicate IP address |
B | VLAN mismatch |
C | TX/RX reverse |
D | Duplex/Speed mismatch |
Question 14 |
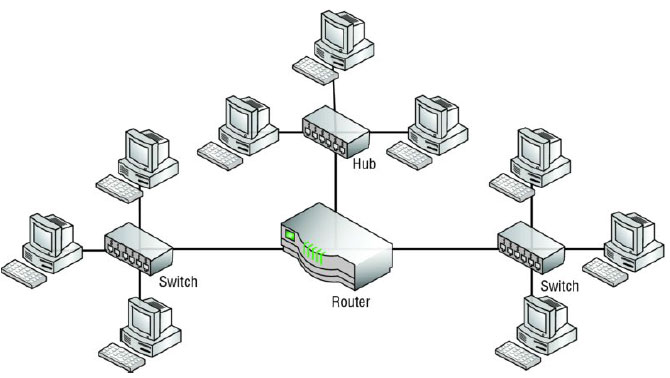
A | There are three collision domains and one broadcast domain. |
B | There are nine collision domains and three broadcast
domains. |
C | There are seven collision domains and three broadcast
domains. |
D | There is one collision domain and one broadcast domain. |
E | There are three collision domains and three broadcast
domains. |
Question 15 |
A | Port 110 |
B | Port 443 |
C | Port 22 |
D | Port 80 |
E | Port 110 |
Question 16 |
A | Coaxial cabling |
B | UTP cabling |
C | STP cabling |
D | Fiber-optic cabling |
Question 17 |
A | tcpdump |
B | arp |
C | dig |
D | nmap |
Question 18 |
A | 2001:0:d58::95:7565:1 |
B | 2001:0:d58:0:0:95:7565:1 |
C | 2001::d58::95:7565:1 |
D | 2001:0:0d58::95:7565:1 |
Question 19 |
A | MD5 |
B | Authentication passphrase |
C | SHA |
D | authpriv |
Question 20 |
A | Replica |
B | Incremental |
C | Snapshots |
D | Differential |
Question 21 |
A | Loopback address |
B | APIPA address |
C | Duplicate MAC addresses |
D | Duplicate IP addresses |
Question 22 |
A | Bridge |
B | Layer 3 switch |
C | Load balancer |
D | Layer 2 switch |
Question 23 |
A | Ports 56 and 57 |
B | Port 123 and 8080 |
C | Ports 67 and 68 |
D | Ports 20 and 21 |
E | Ports 80 and 443 |
Question 24 |
A | IDS firewall |
B | DDoS |
C | DNS sinkhole |
D | MITM |
E | DDoS |
Question 25 |
A | Trojan horse |
B | Logic bomb |
C | Social engineering |
D | Insider threat |
E | Session hijacking |
Question 26 |
A | Because secure protocols would reject malicious packets |
B | Because a secure firewall will protect the device |
C | Because SCP is not a secure service |
D | Because FTP is not a secure service |
Question 27 |
A | Layer 6 - Presentation |
B | Layer 7 – Application |
C | Layer 1 – Physical |
D | Layer 3 – Network |
E | Layer 4 – Transport |
Question 28 |
A | DHCP lease time |
B | TTL |
C | IP helper |
D | Ping table |
E | DNS record type |
Question 29 |
A | Jumbo frames |
B | Clustering |
C | TCP offloading |
D | Round robin |
E | Load balancer |
Question 30 |
A | IEEE 802.1q |
B | IEEE 802.1X |
C | IEEE 802.3x |
D | IEEE 802.11ac |
Question 31 |
A | Credentials |
B | VNC application |
C | Kerberos |
D | Geotagging application |
Question 32 |
A | IP helper |
B | MAC reservation |
C | DHCP timer |
D | Pool |
E | Lease time |
Question 33 |
A | DHCP |
B | DNS |
C | LADP |
D | HTTP |
E | ICMP |
Question 34 |
A | WPA-PSK |
B | EAP-TLS |
C | AES-CCMP |
D | WEP-TKIP |
Question 35 |
A | Switch |
B | Next-generation firewall |
C | Multilayer switch |
D | Bridge |
Question 36 |
A | Jumbo frames |
B | iSCSI |
C | QoS tags |
D | Port aggregation |
Question 37 |
A | Disable DHCP service on the server |
B | Disable Telnet service on the server |
C | Disable FTP service on the server |
D | Disable the SMTP service on the server |
Question 38 |
A | 802.11a |
B | 802.11ac |
C | 802.11b |
D | 802.11n |
Question 39 |
A | Multimeter |
B | Punchdown tool |
C | Tone generator |
D | Loopback adapter |
Question 40 |
A | Multimeter |
B | Protocol analyzer |
C | Tone generator |
D | Spectrum analyzer |
E | OTDR |
Question 41 |
A | Cat 6 |
B | Cat 6a |
C | Cat 5e |
D | Cat 7 |
Question 42 |
A | SFTP |
B | Telnet |
C | TFTP |
D | SSL |
E | FTPS |
Question 43 |
A | Create a network baseline |
B | Create a rack diagram |
C | Create an inventory database |
D | Create a port location diagram |
Question 44 |
A | DSL modem |
B | Access point |
C | Wireless router |
D | Demarc |
E | DOCSIS modem |
Question 45 |
A | Network switch |
B | Media converter |
C | Wireless access point |
D | Firewall |
E | Router |
Question 46 |
A | It provides a faster port to all servers |
B | It segments broadcast domains in the network infrastructure |
C | It provides multiple broadcast domains within a single collision domain |
D | It provides multiple collision domains on one switchport |
Question 47 |
-WLAN architecture supporting speeds in excess of 150 Mbps
-Client less remote network access
-Port-based network access control
A | 802.11n, SSL-VPN, 802.1x |
B | 802.11g, MS-CHAP, 802.16 |
C | 802.11a, IPSec VPN, 802.1x |
D | 802.11b, PPTP,802.1x |
E | 802.11ac, MPLS, 802.3 |
Question 48 |
A | Rogue DHCP server |
B | Expired IP address |
C | Exhausted dynamic scope |
D | Misconfigured VLSM |
Question 49 |
A | Label existing systems with current hostnames |
B | Forward the DHCP logs to the security manager every day |
C | Implement a standardized UNC |
D | Enforce port security to require system authentication |
Question 50 |
A | The utility company throttles power during peak hours |
B | There is interference with the smart reader |
C | An IoT device is causing a DoS attack on the wireless network |
D | There is additional data being transferred over the wireless network |
Question 51 |
A | RADIUS server |
B | Content filter |
C | Wireless controller |
D | VoIP PBX |
Question 52 |
A | 48 collision domains, 5 broadcast domains |
B | 5 collision domains, 48 segments |
C | 240 usable IP addresses |
D | 48 networks, 5 segments |
E | 240 private networks |
Question 53 |
A | 10GBaseT |
B | 1000BaseT |
C | 1000BaseSX |
D | 1000BaseLX |
E | 10Base2 |
F | 10Base5 |
Question 54 |
A | Motion detectors |
B | Video surveillance |
C | Door locks |
D | Biometric scanners |
Question 55 |
A | /all |
B | eth_addr |
C | -i address |
D | -a |
Question 56 |
IP: 192.168.1.100
Mask: 255.255.255.0
Router: 192.168.1.1
A | Interference |
B | Wrong SSID |
C | Channel overlap |
D | Security type mismatch |
Question 57 |
A | The finance department should have 172.16.49.127 as a broadcast address. |
B | The marketing department should receive a /25 network. |
C | The R&D department should have a last usable IP address of 172.16.49.190. |
D | The marketing department should have usable IPs ranging from 172.16.49.129 to 172.16.49.190. |
E | The R&D department should have 172.16.49.207 as a broadcast address. |
F | The legal department should have usable IPs ranging from 172.16.49.129 to 172.16.49.190. |
G | The legal department should have a first usable IP address of 172.16.49.190. |
H | The R&D department should receive a /27 network. |
Question 58 |
A | Equipment closet |
B | Server room |
C | Demarcation point |
D | Intermediate distribution frame |
Question 59 |
A | 10.0.0.0/24 |
B | 10.8.0.0/20 |
C | 10.8.0.0/16 |
D | 10.8.0.0/19 |
Question 60 |
A | 5GHz |
B | 56MHz |
C | 900MHz |
D | 2.4 GHz |
Question 61 |
A | Sign-in sheets |
B | Swipe badges |
C | Motion sensors |
D | Video cameras |
Question 62 |
A | Encrypts network connection. |
B | Enables remote login and command execution. |
C | Provides username & password authentication. |
D | Transmits data in an unencrypted form. |
E | It cannot be used on modern Windows computers. |
F | It does not provide authentication. |
Question 63 |
A | 12 |
B | 14 |
C | 15 |
D | 13 |
E | 3 |
Question 64 |
A | BPDUs entering the root bridge are ignored. |
B | Broadcast storms entering from a root port are blocked. |
C | Loop protection is enabled on the root port of a switch. |
D | The STP root bridge cannot be changed. |
Question 65 |
A | Use an FTP server and provide the file hash. |
B | Use a TFTP server and UDP protocol. |
C | Use a modem and dial-up connection. |
D | Use an HTTP server to share the file. |
Question 66 |
A | 6 |
B | 0 |
C | 1 |
D | 12 |
E | 2 |
Question 67 |
A | Using a secure SSH connection over the WAN link to connect to a server. |
B | Implementing a modem on the AUX port to access a network device. |
C | Telnet into the router over a secure VPN. |
D | Accessing a DSL router via the console port. |
Question 68 |
A | Changing the management software's default port |
B | Replacing the management software's self-signed certificate with a valid certificate |
C | Disabling unnecessary services from the server and management software |
D | Changing the management software's default credentials |
Question 69 |
A | Tone generator |
B | Multimeter |
C | Cable tester |
D | Loopback adapter |
Question 70 |
A | Star |
B | Ad hoc |
C | Ring |
D | Mesh |
Question 71 |
A | Cat 7 |
B | Single-mode |
C | Plenum |
D | PVC |
Question 72 |
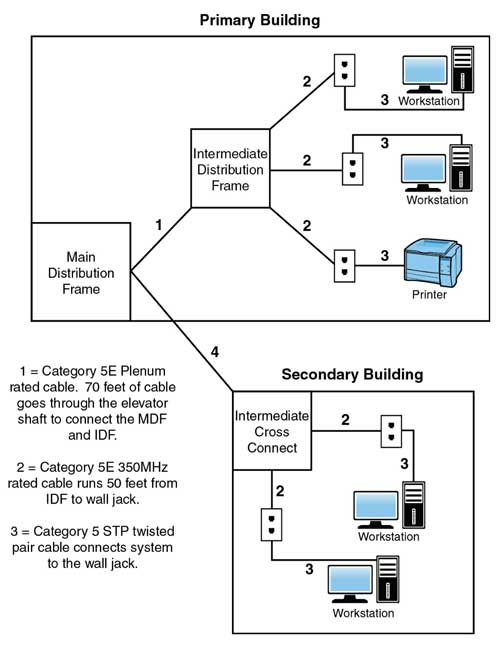
A | Cable 2 should be an STP cable. |
B | Cable 1 does not need to be plenum rated. |
C | Cable 3 should be an STP cable. |
D | None, the network looks good. |
Question 73 |
A | Packet sniffer |
B | Multimeter |
C | OTDR |
D | Spectrum analyzer |
Question 74 |
A | DDoS attacks are launched from multiple hosts |
B | DDoS attacks target multiple networks |
C | Spoofing attacks require physical presence |
D | Spoofing attacks originate from a single host |
Question 75 |
A | ipconfig /all |
B | ipconfig /release |
C | ipconfig /flushdns |
D | ipconfig /renew |
Question 76 |
A | 10.233.2.0/23 |
B | 192.168.25.0/24 |
C | 172.16.0.0/22 |
D | 10.5.4.0/22 |
E | 172.18.0.0/23 |
Question 77 |
A | TLS |
B | SFTP |
C | SSH |
D | LDAP |
Question 78 |
A | CSMA |
B | Analog modem |
C | Broadband |
D | Baseband |
Question 79 |
A | Kerberos |
B | MFA |
C | NAC |
D | Certificate |
E | SSO |
F | RADIUS |
Question 80 |
User A
IP address: 192.168.1.121
Subnet mask: 255.255.255.0
Default gateway: 192.168.1.1
User B
IP address: 192.168.1.125
Subnet mask: 255.255.248.0
Default gateway: 192.168.1.1
A | There is no problem identifiable by the values given. |
B | User B's IP address is not a loopback address |
C | The default gateway should have different values |
D | The subnet values should be the same |
Question 81 |
A | MDI-X |
B | ASIC |
C | SFP |
D | GBIC |
E | SPF |
Question 82 |
A | Data link |
B | Transport |
C | Presentation |
D | Session |
Question 83 |
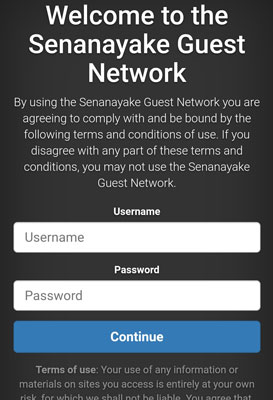
A | SSL certificate |
B | Captive portal |
C | WPA2 |
D | MAC filtering |
E | EAP-TLS |
Question 84 |
A | EMI |
B | Open/short |
C | TX/RX reverse |
D | Attenuation |
Question 85 |
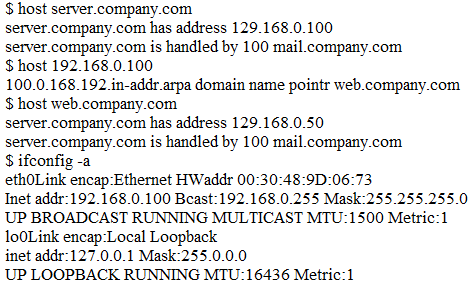
A | The reverse DNS entry is pointing to a different host |
B | The DNS lookup entry is incorrectly configured |
C | There is no reverse DNS entry for this host |
D | The server IP address is incorrectly configured |
Question 86 |
Subnet 1: 192.168.1.0/26
Subnet 2: 192.168.1.65/26
Company B uses the following scheme:
Subnet 1: 192.168.1.50/28
A | VLAN |
B | DMZ |
C | PAT |
D | NAT |
Question 87 |
A | One of the wireless access points is on the wrong frequency |
B | The students are using more than one wireless device port seat |
C | Distance limitations are preventing the students from connecting |
D | The students are attempting to connect 802.11g devices |
Question 88 |
A | PTP |
B | SSL VPN |
C | PPTP |
D | IPSec |
Question 89 |
A | AAAA |
B | CNAME |
C | MX |
D | SRV |
Question 90 |
A | HTTP |
B | ICMP |
C | NetBIOS |
D | DNS |
E | DHCP |
Question 91 |
A | Ad hoc |
B | Partial mesh |
C | Ring |
D | Bus |
Question 92 |

Which of the following ones should the technician use to place the webserver and which of the following firewall rules should the technician configure?
A | Place the web server in the private zone with an inbound rule from eth2 interface to eth1 to accept traffic over port 80 designated to the webserver |
B | Place the web server in the DMZ with an inbound rule from eth1 interface to eth0 to accept traffic over port 80 designated to the webserver |
C | Place the web server in the public zone with an inbound rule from eth0 interface to accept traffic over port 80 designated to the webserver |
D | Place the web server in the DMZ with an inbound rule from eth0 interface to eth1 to accept traffic over port 80 designated to the webserver |
Question 93 |
A | IDF/MDF documentation |
B | Change management |
C | Physical diagram |
D | Performance baseline |
Question 94 |
A | Set the AP to half-duplex to compensate for signal loss |
B | Replace the UTP cable with plenum cable |
C | Upgrade the cable from Cat 5 to Cat 5e or Cat 6 |
D | Install a repeater to boost the signal to its destination |
Question 95 |
A | Adding a router prevents computers on one LAN from communicating with computers on another LAN. |
B | Adding a router reduces the amount of broadcast traffic on each of the two LANs. |
C | Adding a router diverts traffic to an alternate path through the network. |
D | Adding a router reduces the amount of unicast traffic on each of the two LANs. |
Question 96 |
A | TDR |
B | Loopback adapter |
C | Spectrum analyzer |
D | OTDR |
Question 97 |
A | TFTP |
B | Samba |
C | Telnet |
D | LDAP |
Question 98 |
A | International export controls |
B | Data loss prevention |
C | Incident response policy |
D | Remote access policies |
E | Licensing restrictions |
Question 99 |
A | traceroute |
B | netstat |
C | Nmap |
D | pathping |
Question 100 |
A | The cable has bent pins |
B | The cable is rollover cable |
C | The cable is damaged |
D | The cable is a Cat 5 cable |
E | The cable is a crossover cable |
Question 101 |
A | Port mirroring |
B | Trunking |
C | Port aggregation |
D | Spanning tree |
Question 102 |
A | BYOD |
B | AUP |
C | NDA |
D | MOU |
Question 103 |
A | Bad port |
B | ACL misconfiguration |
C | Crosstalk |
D | Duplex/speed mismatch |
Question 104 |
A | TACACS+ |
B | Captive portal |
C | RADIUS |
D | Single sign-on |
Question 105 |
A | Require a pre-shared key for authentication to the wireless network |
B | Implement a Faraday cage within the building premises |
C | Use MAC filtering for authorization to the wireless network |
D | Require PEAP for authentication to the wireless network |
Question 106 |
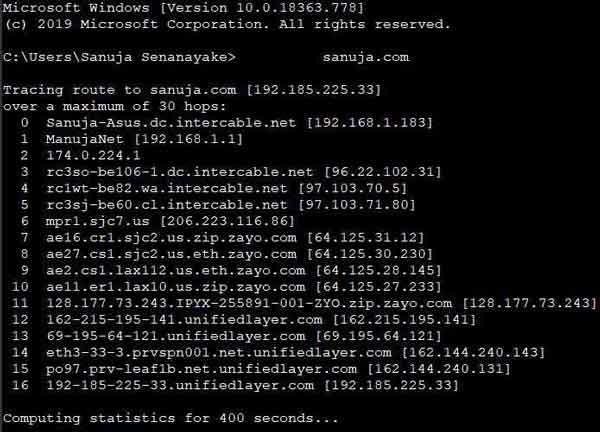
A | nbtstat |
B | netstat |
C | nslookup |
D | pathping |
Question 107 |
A | Adding a fingerprint reader and retina scanner |
B | Adding a fingerprint reader to each workstation and providing a RSA authentication token |
C | Using a smart card and RSA token |
D | Enforcing a stronger password policy and using a hand geometry scan |
Question 108 |
A | 802.3at |
B | 802.1q |
C | 802.1X |
D | 802.3af |
E | 802.11ac |
Question 109 |
A | PEAP |
B | EAP-TLS |
C | Captive portal |
D | WP2-PSK |
Question 110 |
A | Frames |
B | Datagrams |
C | Segments |
D | Packets |
Question 111 |
A | Document the findings and outcomes |
B | Establish a theory of probable cause |
C | Implement the solution |
D | Do nothing |
E | Escalate the ticket to a senior technician |
Question 112 |
A | Connect the switches with a cable that has a TIA/EIA 586A wired connector end and a TIA/EIA 586B wired end. |
B | Replace the new switch with a hub to ensure Layer1 connectivity on the new network segment. |
C | Move the straight-through Ethernet cable connecting the switches to the first port on both switches. |
D | Add a second cable connecting the switches for redundancy and disabling STP on both switches. |
Question 113 |
A | 1000BaseLX SFP |
B | Duplex GBIC |
C | Duplex SFP+ |
D | Bidirectional SFP |
Question 114 |
A | Acceptable use |
B | Asset disposal |
C | Incident response |
D | Data loss prevention |
Question 115 |
A | 1022 |
B | 2046 |
C | 1024 |
D | 510 |
E | 2048 |
F | 512 |
Question 116 |
A | Identification card |
B | Biometric device |
C | Proximity reader |
D | Video camera |
Question 117 |
A | device hardening. |
B | penetration testing. |
C | risk assessment. |
D | role separation. |
Question 118 |
A | The ports are associated with deprecated services |
B | The ports replied with a SYN/ACK response |
C | The ports belong to an active system and are denying requests |
D | The ports do not belong to a live system |
Question 119 |
A | SSH over IPsec client-to-site VPN |
B | Telnet over PSTN |
C | HTTP over WPA2-TKIP WiFi |
D | RDP over SSLv2 HTTPS terminal services gateway |
Question 120 |
A | The technician should check the internal diagnostics on all the phones to look for a common thread |
B | The technician should use a packet tracer to see if the traffic is getting out of the network |
C | The technician should reset all the phones and deprovision information from the provider |
D | The technician should run ping tests on the Internet line to monitor for packet loss and latency |
Question 121 |
A | SVC |
B | BRI |
C | SNR |
D | RFI |
Question 122 |
A | Proxy service |
B | Dynamic DNS |
C | Content filtering |
D | Intrusion detection |
Question 123 |
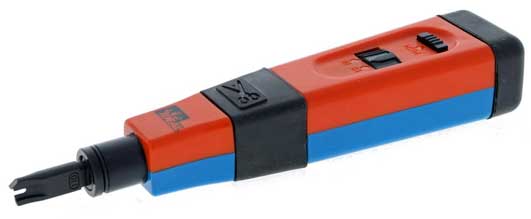
Image Credits: https://www.homedepot.com/p/ Ideal-Punchdown-Tool- with-110-and-66- Blades-35-485/ 203761571
A | Butt set |
B | Crimper |
C | Tone generator and locator |
D | Punchdown tool |
Question 124 |
A | network devices |
B | traffic-routing protocols |
C | public/private networks |
D | packet flow |
Question 125 |
A | Replace the server's single-mode fiber cable with multimode fiber |
B | Use a TDR to test both strands of a new replacement cable prior to connecting it to the server |
C | Move the fiber cable to a different port on the switch where both strands function |
D | Reverse the fiber strands of the cable and reconnect them to the server |
Question 126 |
A | IP |
B | TCP |
C | Ethernet |
D | None of the answers are correct. |
E | UDP |
Question 127 |
A | Frequency mismatch |
B | Latency |
C | Jitter |
D | Attenuation |
Question 128 |
A | Perform a traceroute command to identify the router that is not functioning. |
B | Configure the DNS address in the DHCP scope to a 10.10.5.0/24 address. |
C | Verify the host has physical connectivity and is on the correct VLAN. |
D | Change the IP scope on the DHCP server to a public IP address range. |
Question 129 |
A | Update firmware |
B | Perform file hashing |
C | Generate new keys |
D | Change default credentials |
Question 130 |
A | AUP |
B | Incident response |
C | Offboarding |
D | Remote access |
E | DLP |
Question 131 |
A | Star |
B | Mesh |
C | Bus |
D | Ring |
Question 132 |
A | Spectrum analyzer |
B | Packet sniffer |
C | nslookup |
D | netstat |
Question 133 |
A | Clustering |
B | NIC teaming |
C | Redundant circuits |
D | Load balancing |
E | Multiple NAT |
Question 134 |
A | Transport |
B | Application |
C | Physical |
D | Network |
Question 135 |
A | NTP |
B | RTP |
C | H.323 |
D | SMB |
E | SIP |
F | ICMP |
Question 136 |
A | Change management |
B | Inventory report |
C | Network diagrams |
D | Labeling report |
Question 137 |
A | Generate new SSH keys |
B | Upgrade to the latest firmware |
C | Review and modify the firewall rules |
D | Verify the default passwords have been changed |
Question 138 |
A | DDoS attack |
B | MITM attack |
C | Session hijacking |
D | Spoofing attack |
E | Wardriving |
Question 139 |
A | Packet filtering utility |
B | Packet tracing utility |
C | MS Windows command-line tool |
D | Packet capturing utility |
E | Linux command-line tool |
Question 140 |
A | iSCSI |
B | OC3 |
C | FCoE |
D | InfiniBand |
Question 141 |
A | Change the switch |
B | Modify the speed and duplex |
C | Plug in to another port |
D | Replace the NIC |
Question 142 |
A | Create a VLAN for all unused switchports. |
B | Implement a DMZ for all external services. |
C | Implement root guard on all switches. |
D | Create a honeypot to attract attackers. |
Question 143 |
A | Demarc |
B | Data tier |
C | IDF |
D | DMZ |
Question 144 |
A | Evil twin |
B | Phishing |
C | OCSP stapling |
D | MITM |
E | DDoS |
Question 145 |
Gigabit Ethernet 1 Interface: 10.10.0.1/24 Serial 0 Interface: 10.10.0.253/30
A | The router was configured with an incorrect loopback address |
B | The router was configured with an incorrect subnet mask |
C | The router was configured with an incorrect default gateway |
D | The router was configured with an incorrect IP address |
Question 146 |
A | Session hijacking |
B | ARP poisoning |
C | Social engineering |
D | Evil twin |
E | DHCP exhaustion |
Question 147 |
A | Rack location |
B | Media type |
C | Room number |
D | Hostname |
Question 148 |
A | Configure modern devices under the 5GHz band while dedicating the 2.4GHz band to legacy devices. |
B | Create two SSIDs, one to support CCMP-AES encryption and one with TKIP-RC4 encryption. |
C | Configure the APs to use LEAP authentication to support WPA rather than WPA2 for full compatibility. |
D | Connect the legacy devices with a PSK while the modern devices should use the more secure EAP. |
Question 149 |
A | Spanning tree |
B | BPDU guard |
C | DHCP snooping |
D | Flood guard |
Question 150 |
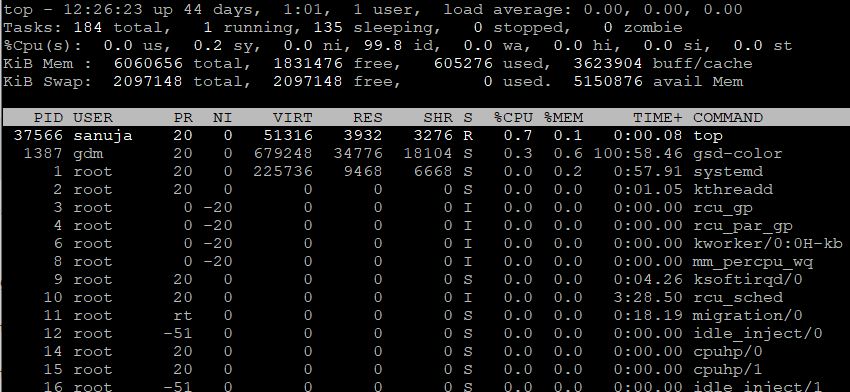
A | gdm |
B | systemd |
C | root |
D | top |
E | sanuja |
Question 151 |
route add 0.0.0.0 mask 0.0.0.0 192.169.1.222 metric 1
A | The technician is adding a static IP address. |
B | The technician is setting the default gateway. |
C | The technician is clearing the route table. |
D | The technician is clearing the subnet mas setting. |
Question 152 |
A | Open wireless |
B | Pre-shared key |
C | Geofencing |
D | MAC filtering |
Question 153 |
A | Broadband cable |
B | PRI |
C | MPLS |
D | Frame relay |
E | ISDN |
Question 154 |
A | Patch cable type |
B | DHCP scope availability |
C | VLAN routing |
D | Server-based firewall configuration issue |
Question 155 |
A | Bridge |
B | Router |
C | Hub |
D | Switch |
Question 156 |
A | SNMP agent |
B | OUI |
C | SNMP host |
D | OTDR |
E | OID |
Question 157 |
A | Enable MAC address filtering on each access point. |
B | Disable the SSID broadcast on each access point. |
C | Enable AP isolation on each access point. |
D | Reduce the TX power on each access point. |
Question 158 |
A | One router connected to one 12-port switch configured for the manager's computers, phones, and printer, and one 12-port switch configured for the other computers, VoIP phones, and printer |
B | One router connected to one 24-port switch configured with three VLANS: one for the manager's computers and printer, one for the other computers and printer, and one for the VoIP phones |
C | One router connected to one 24-port switch configured with two VLANS: one for the manager's computers, VoIP phones, and printer, and one for the other computers, VoIP phones, and printer |
D | Two routers with each router connected to a 12-port switch, with a firewall connected to the switch connected to the manager's desktop computers, VoIP phones, and printer |
Question 159 |
A | Route redistribution |
B | Routing loop |
C | Routing table |
D | DHCP |
E | Dynamic routes |
Question 160 |
A | CSR |
B | CRL |
C | OCSP |
D | Key escrow |
Question 161 |
A | Bridge |
B | Signal repeater |
C | Layer 3 switch |
D | Domain server |
E | Layer 2 switch |
Question 162 |
A | Add a redundant power supply to the switch |
B | Install a power converter for the switch |
C | Implement stacking on the switches in the rack |
D | Add a second UPS into the rack |
Question 163 |
A | The LAN and WLAN should be configured in the same zone with dynamic DENY ALL rules. |
B | The LAN and WLAN should be configured in separate zones with a firewall in between. |
C | The LAN and WLAN should be configured in the DMZ so traffic is denied automatically. |
D | The LAN and WLAN should be marked as trusted during work hours and untrusted during off hours. |
Question 164 |
A | WAP power level controls |
B | Network mapper |
C | Protocol analyzer |
D | Logical network diagram |
Question 165 |
A | The Faraday cage is creating attenuation of the cellular network. |
B | The Faraday cage is creating interference within the bookstore. |
C | The Faraday cage is creating latency on the cellular network. |
D | The Faraday cage prevents access by redirecting signals. |
Question 166 |
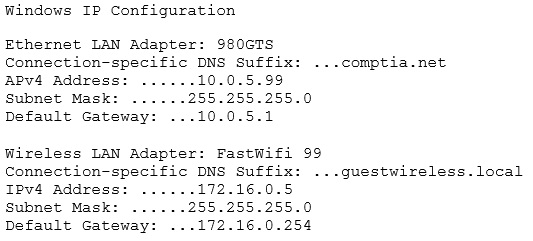
Which of the following would MOST likely allow the network drives to be accessed?
A | Check the wireless DHCP configuration |
B | Disable the LAN adapter |
C | Disable the WLAN adapter |
D | Update the WLAN adapter driver |
Question 167 |
A | Speed |
B | MTU |
C | Duplex |
D | TTL |
Question 168 |
A | Point-to-multipoint |
B | Client-to-site |
C | Point-to-point |
D | Site-to-site |
Question 169 |
A | Bluesnarfing |
B | VLAN hopping |
C | MAC spoofing |
D | Man-in-the-middle |
E | Session hijacking |
Question 170 |
A | permit tcp any any eq 8080 |
B | permit tcp any any eq 110 |
C | permit udp any any eq 68 |
D | permit tcp any any eq 20 |
E | permit udp any any eq 53 |
F | permit udp any any eq 25 |
Question 171 |
A | MOU |
B | AUP |
C | NDA |
D | SLA |
Question 172 |
A | Secure the area |
B | Implement a chain of custody |
C | Take pictures upon arrival |
D | Document the scene |
Question 173 |
A | Open/short on the cable |
B | Transceiver mismatch |
C | Crosstalk |
D | Jitter |
Question 174 |
A | Change management |
B | Network diagram |
C | Network configuration |
D | Rack diagram |
Question 175 |
A | SaaS |
B | IaaS |
C | NAS |
D | SAN |
Question 176 |
A | arp |
B | dig |
C | ipconfig |
D | nslookup |
Question 177 |
A | DLP |
B | AUP |
C | SLA |
D | NDA |
Question 178 |
A | Channel 10 |
B | Channel 7 |
C | Channel 6 |
D | Channel 9 |
Question 179 |
A | CHAP |
B | SNMP |
C | FTP |
D | SSL |
E | SSH |
Question 180 |
A | Digital signatures |
B | Digital signatures |
C | SSL certificate |
D | 3DES encryption |
Question 181 |
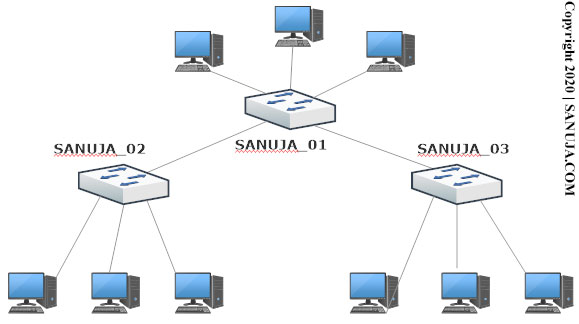
A | There is one collision domain for this network. |
B | There are 12 collision domains, one for each switch connection. |
C | There are 3 collision domains, one for each switch-to-switch connection. |
D | There are 9 collision domains, one for each half-duplex connection. |
Question 182 |
A | DHCP reservation for the laptops MACs |
B | Additional lease time for the laptop computers |
C | CNAME record in the users dynamic DNS accounts |
D | IP helper relay system for configuration hops |
Question 183 |
A | The use of autonomous APs with a wireless controller |
B | The use of lightweight APs with a load balancer |
C | The use of lightweight APs with a wireless controller |
D | The use of autonomous APs with a load balancer |
Question 184 |
A | VLAN mismatch |
B | Bent pins |
C | Damaged cables |
D | TX/RX reverse |
E | Duplex mismatch |
F | Crosstalk |
Question 185 |
A | Port 25 |
B | Port 123 |
C | Port 161 |
D | Port 69 |
Question 186 |
A | SFTP |
B | RDP set to console connection |
C | SSH in tunnel mode |
D | EAP-PEAP |
Question 187 |
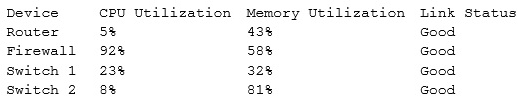
Which of the following devices is causing the issue?
A | Switch 2 |
B | Router |
C | Firewall |
D | Switch 1 |
Question 188 |
A | PTR |
B | A |
C | MX |
D | NS |
E | CNAME |
Question 189 |
A | SMB |
B | SSL |
C | RDP |
D | NTP |
E | SNMP |
Question 190 |
A | Proxy server |
B | Router |
C | Load balancer |
D | Switch |
Question 191 |
A | DSCP |
B | VLANs |
C | SIP |
D | STP |
Question 192 |
A | Server IP address |
B | Host-based firewall settings |
C | DNS SRV record |
D | TACAS+ server time |
Question 193 |
A | Backs up files with the archive bit set but does not clear the bit. |
B | Backs up files with a date earlier than today’s date with a clear archive bit. |
C | Backs up files with the creation or modified date as the current date. |
D | Backs up all files and sets the archive bit. |
Question 194 |
A | TFTP |
B | SCP |
C | DHCP |
D | Telnet |
E | FTP |
Question 195 |
A | 192.168.12.97 to 255.255.255.224 |
B | 192.168.12.97 to 255.255.255.240 |
C | 192.168.12.97 to 255.255.255.192 |
D | 192.168.12.97 to 255.255.255.248 |
Question 196 |
A | RG-6 |
B | Cat 6 |
C | SMF |
D | Cat 3 |
E | Cat 5 |
Question 197 |
A | Establish a plan of action |
B | Gather information |
C | Document the findings |
D | Determine the symptoms |
Question 198 |
A | IDS |
B | IPS |
C | VPN concentrator |
D | Load balancer |
E | Proxy server |
Question 199 |
A | SOHO router |
B | DNS server |
C | Cable modem |
D | Layer 2 switch |
Question 200 |
A | VPC |
B | Fiber Channel |
C | vSAN |
D | Virtual switch |
E | FCoE |
← |
List |
→ |
| 1 | 2 | 3 | 4 | 5 |
| 6 | 7 | 8 | 9 | 10 |
| 11 | 12 | 13 | 14 | 15 |
| 16 | 17 | 18 | 19 | 20 |
| 21 | 22 | 23 | 24 | 25 |
| 26 | 27 | 28 | 29 | 30 |
| 31 | 32 | 33 | 34 | 35 |
| 36 | 37 | 38 | 39 | 40 |
| 41 | 42 | 43 | 44 | 45 |
| 46 | 47 | 48 | 49 | 50 |
| 51 | 52 | 53 | 54 | 55 |
| 56 | 57 | 58 | 59 | 60 |
| 61 | 62 | 63 | 64 | 65 |
| 66 | 67 | 68 | 69 | 70 |
| 71 | 72 | 73 | 74 | 75 |
| 76 | 77 | 78 | 79 | 80 |
| 81 | 82 | 83 | 84 | 85 |
| 86 | 87 | 88 | 89 | 90 |
| 91 | 92 | 93 | 94 | 95 |
| 96 | 97 | 98 | 99 | 100 |
| 101 | 102 | 103 | 104 | 105 |
| 106 | 107 | 108 | 109 | 110 |
| 111 | 112 | 113 | 114 | 115 |
| 116 | 117 | 118 | 119 | 120 |
| 121 | 122 | 123 | 124 | 125 |
| 126 | 127 | 128 | 129 | 130 |
| 131 | 132 | 133 | 134 | 135 |
| 136 | 137 | 138 | 139 | 140 |
| 141 | 142 | 143 | 144 | 145 |
| 146 | 147 | 148 | 149 | 150 |
| 151 | 152 | 153 | 154 | 155 |
| 156 | 157 | 158 | 159 | 160 |
| 161 | 162 | 163 | 164 | 165 |
| 166 | 167 | 168 | 169 | 170 |
| 171 | 172 | 173 | 174 | 175 |
| 176 | 177 | 178 | 179 | 180 |
| 181 | 182 | 183 | 184 | 185 |
| 186 | 187 | 188 | 189 | 190 |
| 191 | 192 | 193 | 194 | 195 |
| 196 | 197 | 198 | 199 | 200 |
| End |
Based on general knowledge and CompTIA guidelines published in 2020.
FAQ | Report an Error
Study outline at: CompTIA Exams Guide
Disclaimer: While every reasonable effort is made to ensure that the information provided is accurate, no guarantees for the currency or accuracy of information are made. It takes several proof readings and rewrites to bring the quiz to an exceptional level. If you find an error, please contact me as soon as possible. Please indicate the question ID-Number or description because server may randomize the questions and answers.