← Exams and Quizzes | Professional Exams →
Notice
If you get a question wrong, you can still click on the other answers. This will open up hints and explanations (if available), which will provide additional information. Exam should be 1 minute per question and please time accordingly.It is not required to have CompTIA A+ certification prior to obtaining CompTIA Network+ certification. It is recommended to have CompTIA A+ certification or the knowledge of the subject matter that is covered under A+ certification exam before taking Network+ certification exam. It is also recommended, but not required, that you have about 12 months of IT networking work experience.
Go to: Set II | Set III
CompTIA Network+ N10-007 - Set I
Congratulations - you have completed CompTIA Network+ N10-007 - Set I.
You scored %%SCORE%% out of %%TOTAL%%. With incorrect multiple attempts, your score is %%PERCENTAGE%%. Your performance has been rated as %%RATING%%
Question 1 |
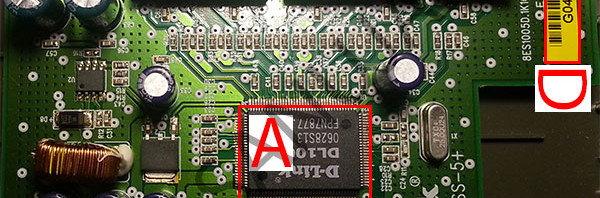
A | Content filter |
B | VPN concentrator |
C | Web application firewall |
D | VLAN restrictions |
E | IPS |
Question 2 |
A | UDP |
B | IGMP |
C | ICMP |
D | TCP |
Question 3 |
A | NAS |
B | InfinitiBand |
C | iSCSI |
D | Fibre Channel |
Question 4 |
A | Throttling |
B | Bandwidth quotas |
C | Data usage limits |
D | Session hijacking |
E | Blocking |
Question 5 |
A | RAID 0 |
B | RAID 5 |
C | RAID 10 |
D | RAID 1 |
Question 6 |
A | STP |
B | NAT |
C | PAT |
D | SNAT |
E | ARP |
Question 7 |
A | dig |
B | tcpdump |
C | iptables |
D | nmap |
Question 8 |
A | BOIS firmware patch |
B | Feature change |
C | Operating system update |
D | Vulnerability patch |
E | Driver update |
Question 9 |
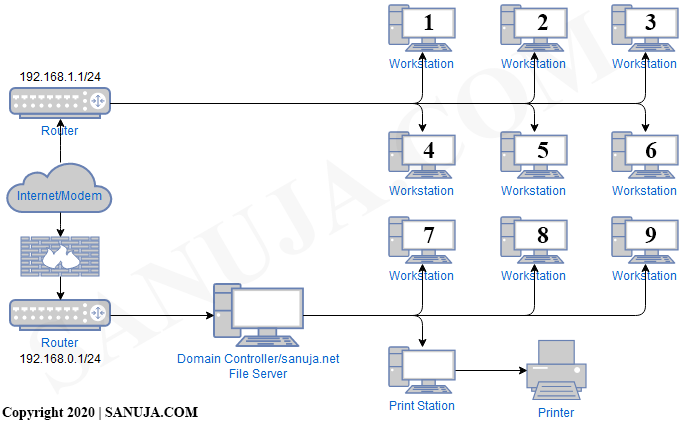
A | 192.168.0.1 |
B | 10.1.0.255 |
C | 10.1.1.255 |
D | 192.168.1.109 |
E | 192.168.0.55 |
Question 10 |
A | Branch-to-server |
B | Host-to-host |
C | Extranet |
D | Site-to-site |
E | Host-to-site |
Question 11 |
A | Control the attenuation of the non-voice traffic across the network links |
B | Control the EMI of the multimedia traffic across the network links |
C | Control the jitter of the affected traffic across the network links |
D | Control the latency of traffic across the network links |
Question 12 |
A | Server clustering |
B | DNS round robin |
C | RAID 1 |
D | Muti-ISP connections |
E | NIC teaming |
Question 13 |
A | A hub |
B | A gateway |
C | A router |
D | A switch |
Question 14 |
A | Configure geofencing |
B | Have the ISP double the bandwidth |
C | Enable WPA and change the SSID |
D | Move from WPA2 to WEP |
Question 15 |
A | Patch and update |
B | Enable port mirroring |
C | Implement spanning tree |
D | Change default admin password |
E | Perform VLAN hopping |
F | Perform backups |
Question 16 |
A | Star |
B | Bus |
C | Ring or circular |
D | Mesh |
E | Point-to-point |
Question 17 |
A | NAT |
B | DDoS |
C | DMZ |
D | RIP |
E | QoS |
Question 18 |
A | VDSL |
B | HDSL |
C | IDSL |
D | RADSL |
Question 19 |
A | 10GBase-CX4 |
B | 10GBase-SR |
C | 10GBase-ER |
D | 10GBase-LR |
E | 10GBase-LX4 |
Question 20 |
A | Gateway |
B | Router |
C | Switch |
D | Bridge |
Question 21 |
A | Geofencing |
B | Social engineering |
C | Asset tracking |
D | Biometric |
E | Tamper detection |
Question 22 |
A | The ticket granting key |
B | The private key |
C | The public key |
D | The secure key |
E | The session key |
Question 23 |
A | Walk a user through troubleshooting the connection |
B | Hire a third-party contractor to go on-site |
C | Use a modem to console into the router |
D | Travel to the branch office |
Question 24 |
A | Hex |
B | Binary |
C | CIDR |
D | Octal |
Question 25 |
A | RADIUS |
B | LDAP |
C | NAC |
D | TKIP-RC4 |
Question 26 |
A | Session |
B | Physical |
C | Data link |
D | Presentation |
E | Transport |
F | Network |
G | Application |
Question 27 |
A | 12 inches |
B | 16 inches |
C | 19 inches |
D | 24 inches |
Question 28 |
A | Network |
B | Data link |
C | Application |
D | Transport |
E | Physical |
F | Presentation |
G | Session |
Question 29 |
A | PaaS |
B | Hosted |
C | IaaS |
D | SaaS |
E | VPN |
Question 30 |
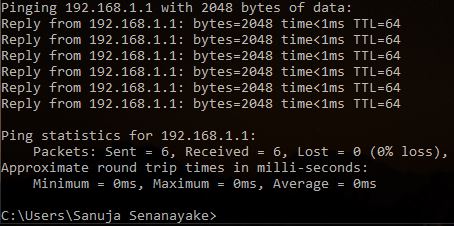
A | ping 192.168.1.1 -l 2048 -t |
B | ping 192.168.1.1 -t |
C | ping 192.168.1.1 -l 2048 -t 6 |
D | ping 192.168.1.1 -l 2048 -n 6 |
E | ping 192.168.1.1 -n 2048 |
Number of messages: -n parameter = 6
Question 31 |
A | Session |
B | Data Link |
C | Physical |
D | Application |
E | Presentation |
F | Network |
G | Transport |
Question 32 |
A | Instead of replacing current units during failures, use parts from the spare units to fix the current unit. |
B | Store all spare equipment in a sepearete office building for extra protection. |
C | Keep purchasing new spare equipment. |
D | Do nothing and keep the spare nearby for an emergency. |
E | Update the firmware and drivers on spare network equipment regularly. |
Question 33 |
A | session hijacking |
B | vulnerability scanning |
C | penetration testing |
D | friendly DoS |
E | social engineering |
Question 34 |
A | Set the firewall to operate in transparent mode |
B | Allow the firewall to accept inbound traffic to ports 25, 67,179, and 3389 |
C | Allow the firewall to accept inbound traffic to ports 21, 53, 69, and 123 |
D | Allow the firewall to accept inbound traffic to ports 80,110,143, and 443 |
Question 35 |
A | Proxy server |
B | Load balancer |
C | Enterprise firewall |
D | Wireless controller |
E | IDS |
Question 36 |
A | Layer 1 |
B | Layer 4 |
C | Layer 3 |
D | Layer 2 |
Question 37 |
A | nmap |
B | tcpdump |
C | netstat |
D | dig |
Question 38 |
A | Captive portal |
B | WPA2 |
C | Access control lists |
D | Port security |
Question 39 |
A | WEP |
B | WPA |
C | WPA2 |
D | 802.1X |
Question 40 |
A | Perform frequent security and vulnerability updates. |
B | Perform frequent IT audits. |
C | Install and maintain advanced enterprise firewall applications. |
D | Configure advance intrusion detection and firewall rules on the main datacenter. |
E | Physical inspection of each site/workstation. |
Question 41 |
A | Dual power supplies |
B | Power redundancy |
C | Power looping |
D | Uninterruptible Power Supply (UPS) |
E | Redundant circuits |
Question 42 |
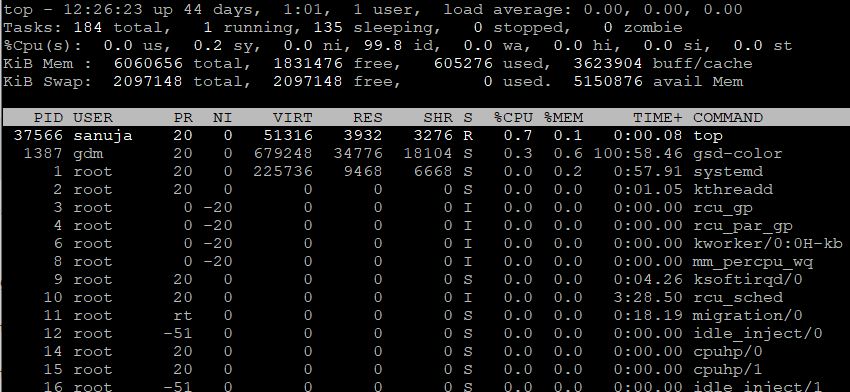
A | cpustat |
B | ping |
C | top |
D | netstat |
E | monitor |
Question 43 |
A | RJ-45 |
B | RG-58 |
C | RJ-11 |
D | RG-8 |
Question 44 |
A | An AUP covering how a personal phone may be used for work matters |
B | Real-time remote monitoring of the phone’s activity and usage |
C | A consent to monitoring policy covering company audits of the personal phone |
D | An NDA ensuring work data stored on the personal phone remains confidential |
Question 45 |
A | NAC |
B | Port security |
C | Captive portal |
D | WAP |
E | MAC filtering |
Question 46 |
A | Encapsulate the storage traffic in a GRE tunnel |
B | Turn off MDIX settings on the NAS and server switchports |
C | Enable jumbo frames on the NAS and server |
D | Utilize UDP to eliminate packet overhead |
Question 47 |
A | Project management |
B | Change management |
C | Standard operating procedure |
D | Process management |
Question 48 |
A | iSCSI |
B | NAS |
C | SAN |
D | FTP |
E | FCoE |
Question 49 |
A | Bridges |
B | Routers |
C | Firewalls |
D | Hubs |
Question 50 |
A | IP |
B | ICMP |
C | IMAP |
D | IGMP |
Question 51 |
A | PAP |
B | CHAP |
C | WEP |
D | MS-CHAPv2 |
E | EAP |
Question 52 |
A | Netstat |
B | Syslog |
C | Top |
D | Netmon |
Question 53 |
A | BYOD |
B | SLA |
C | NDA |
D | IRP |
Question 54 |
A | TKIP |
B | LDAP |
C | Radius |
D | 802.1X |
E | Kerberos |
Question 55 |
A | RC5 |
B | USB 3.0 |
C | RJ45 |
D | USB 2.0 |
E | DB9 |
Question 56 |
A | MSS |
B | WinMS |
C | MMS |
D | Window |
Question 57 |
A | DHCP exclusion |
B | DHCP relay |
C | DHCP option |
D | DHCP reservation |
E | DHCP restriction |
Question 58 |
A | tracert |
B | netstat |
C | ping |
D | ipconfig |
E | ifconfig |
Question 59 |
A | Reference the ARP table in the router. |
B | Set up an SSH session to the desktop. |
C | Configure port security on the switch. |
D | Perform a DNS lookup on the server. |
Question 60 |
A | CNAME |
B | MD |
C | PTR |
D | MX |
E | A |
Question 61 |
A | Permit 192.168.1.143 port143 |
B | Permit 192.168.1.143 port 25 |
C | Permit 192.168.1.143 port 80 |
D | Permit 192.168.1.143 port 443 |
E | Permit 192.168.1.143 port 587 |
F | Permit 192.168.1.143 port 110 |
Question 62 |
A | HTTP |
B | UDP |
C | TCP |
D | IP |
Question 63 |
A | Physical network diagram |
B | Asset management files |
C | Logical network diagram |
D | Wiring schematic |
E | MSConfig file |
Question 64 |
A | -a |
B | -n |
C | -t |
D | -i |
Question 65 |
A | DDoS |
B | Spoofing |
C | Phishing |
D | Ransomware |
E | Session hijacking |
Question 66 |
A | Face geometry |
B | Tamper detection |
C | Biometrics |
D | Geofencing |
E | Pattern recognition |
Question 67 |
A | Switch |
B | Bridge |
C | Router |
D | Hub |
Question 68 |
A | Enterrpise APs |
B | Coaxial cabling |
C | Twisted pair cabling |
D | Fiber-optic cabling |
Question 69 |
A | Ring |
B | Ad hoc |
C | Bus |
D | Mesh |
E | Star |
Question 70 |
A | Multimeter |
B | Loopback adapter |
C | Cable tester |
D | Tone generator |
Question 71 |
A | Smartcards |
B | Motion detection |
C | Biometrics |
D | Video surveillance |
Question 72 |
A | Collision domains occur in layer 1 while broadcast domains occur in layer 2. |
B | It is impossible to have a collision domain in a wired (LAN) network infrastructure. |
C | Both broadcast and collision domains occur at layer 2. |
D | It is impossible to have a collision domain in a wireless network infrastructure. |
E | Broadcast domains occur in layer 1 while collision domains occur in layer 2. |
Question 73 |
A | Accounting |
B | Auditing |
C | Authentication |
D | Authorization |
Question 74 |
A | 192.168.1.1 |
B | 255 255 255.0 |
C | 255 255 255.0 |
D | 192.168.1.0 |
E | 192.168.0.55 |
Question 75 |
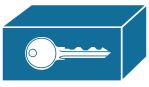
A | Encryption key |
B | Authentication server |
C | VPN gateway |
D | HTTPS server |
E | Secure server |
Question 76 |
A | Preshared |
B | Private |
C | Public |
D | Secured |
E | Privileged |
Question 77 |
A | Proxy server |
B | UTM appliance |
C | VoIP gateway |
D | VPN concentrator |
Question 78 |
A | Encryption |
B | Certification |
C | Authentication |
D | Authorization |
E | Enrollment |
Question 79 |
A | Application |
B | Data Link |
C | Network |
D | Session |
E | Transport |
Question 80 |
A | Wardriving |
B | Social engineering |
C | Logic bomb |
D | Evil twin |
Question 81 |
A | Wiring schematic |
B | Logical network diagram |
C | Physical network diagram |
D | Circuit diagrams |
E | Asset management files |
Question 82 |
A | Administration |
B | Accounting |
C | Authorization |
D | Authentication |
Question 83 |
A | arp -c |
B | arp -s |
C | arp -a |
D | arp -d |
E | arp -t |
Question 84 |
A | Centimeters |
B | Units |
C | Inches |
D | Millimeters |
E | Number of screw holes |
Question 85 |
A | Layer 1 |
B | Layer 5 |
C | Layer 4 |
D | Layer 2 |
E | Layer 6 |
F | Layer 7 |
G | Layer 3 |
Question 86 |
A | RJ45 |
B | MTRJ |
C | F-type |
D | RJ11 |
E | ST |
Question 87 |
A | 1024 |
B | 50134 |
C | 1999 |
D | 80 |
E | 995 |
F | 23 |
Question 88 |
A | Circuit labeling |
B | Airflow and cooling |
C | Power redundancy |
D | UPS capability |
Question 89 |

Image Credit: https://www.tequipment.net/ FlukeNetworks52801009.html
A | When you place the tool at one end of a wire, it generates a tone that can be detected at the other end. |
B | By touching the end of the tool to a copper cable, you can detect and measure the electrical current flowing through it. |
C | By connecting the clips to pins in a punchdown block, you can access telephone circuits in order to test them or place telephone calls. |
D | To attach a bulk cable end to an RJ45 connector, you use the tool to squeeze the connector closed, forcing the wire ends to contact the connector’s pins. |
Question 90 |
A | Class D |
B | Class C |
C | Class B |
D | Class A |
E | None of the classes |
Question 91 |
A | Protocol analyzer |
B | Layer 3 switch |
C | NAT |
D | Layer 7 firewall |
E | Web proxy |
Question 92 |
A | Cross talk |
B | Wrong passphrase |
C | Channel overlap |
D | Overcapacity |
Question 93 |
A | arp -s |
B | arp -a |
C | arp -c * |
D | arp -d * |
Question 94 |
A | 2 |
B | 6 |
C | 7 |
D | 0 |
E | 4 |
Question 95 |
A | LC to SC |
B | ST to ST |
C | SC to SC |
D | SC to ST |
E | LC to ST |
Question 96 |
A | ISDN |
B | Cable broadband |
C | DSL |
D | Dial-up modem |
Question 97 |
A | Logical network diagram |
B | Circuit diagrams |
C | Asset management files |
D | Wiring schematic |
E | Physical network diagram |
Question 98 |
A | Patch panel |
B | 110 block |
C | CMTS |
D | 66 block |
E | Fiber distribution panel |
Question 99 |
A | ACL |
B | Sticky MAC |
C | NAC |
D | NAT |
E | 802.1x |
Question 100 |
A | RAID 1 |
B | Clustering |
C | UPS |
D | SNMP |
Question 101 |
A | BNC |
B | RJ45 |
C | MTRJ |
D | 8P8C |
E | F-type |
Question 102 |
A | device hardening |
B | biometrics |
C | asset tracking |
D | tamper detection |
E | hardware security |
Question 103 |
A | 990 |
B | 443 |
C | 80 |
D | 25 |
E | 110 |
Question 104 |
A | MX |
B | TXT |
C | NS |
D | AAAA |
E | A |
Question 105 |
A | A private IP pointing to the web front end |
B | A private IP pointing to the web proxy |
C | A static IP pointing to the passive DB |
D | A virtual IP pointing to the active DB |
Question 106 |
A | Point-to-multipoint |
B | Mesh |
C | Peer-peer |
D | Bus |
E | Point-to-point |
F | Ring |
Question 107 |
A | NAT |
B | VIP |
C | SIP |
D | PAT |
Question 108 |
A | 80 , 443 |
B | 143 , 993 |
C | 161 , 162 |
D | 5060 , 3389 |
E | 5060 , 5061 |
Question 109 |
A | T-1 |
B | T-3 |
C | OC-1 |
D | E-1 |
Question 110 |
A | dig |
B | ifconfig |
C | route |
D | netstat |
E | traceroute |
Question 111 |
A | A user application problem |
B | A wide area newtwork problem |
C | A shared resource problem |
D | A network-wide problem |
E | A system-wide problem |
Question 112 |
A | Layer 2 router |
B | Layer 3 repeater |
C | Ethernet hub |
D | Multiport bridge |
Question 113 |
A | DHCP server issue |
B | Duplex/speed mismatch |
C | VLAN mismatch |
D | DNS server issue |
E | Spanning tree blocked ports |
Question 114 |
A | https://sanuja.com/123456 |
B | https://sanuja.com:123456 |
C | http://sanuja.com/123456 |
D | http://sanuja.com:123456 |
E | None of the answers are correct because you cannot assign random port numbers. |
Question 115 |
A | traceroute |
B | netstat |
C | ifconfig |
D | ping |
Question 116 |
A | WPA2 |
B | RADIUS |
C | EAP-TLS |
D | Kerberos |
Question 117 |
A | Change the default credentials |
B | Disable unused switchports |
C | Apply patches and updates |
D | Verify the firmware file hash |
Question 118 |
A | MDF |
B | TDM |
C | VRF |
D | IDF |
Question 119 |
A | Logic bomb |
B | Social engineering |
C | Evil twin |
D | Wardriving |
Question 120 |
A | Multiport |
B | Transparent |
C | Source route |
D | Store and forward |
Question 121 |
A | BGP |
B | SIP |
C | LACP |
D | LLDP |
Question 122 |
A | ICMP |
B | IP |
C | Ethernet |
D | TCP |
E | UDP |
Question 123 |
A | DSL |
B | BRI |
C | E1/E3 |
D | PRI |
Question 124 |
A | Voice over IP |
B | Round-robin DNS |
C | Quality of service |
D | CARP |
Question 125 |
A | TKIP |
B | 802.1X |
C | RC4 |
D | AES |
E | Kerberos |
Question 126 |
A | 192.168.1.1 |
B | 175.168.0.255 |
C | 192.168.0.1 |
D | 175.255.255.255 |
E | 169.254.54.5 |
Question 127 |
A | VLAN hopping is the act of exploiting poor VLAN tagging. Session hijacking is a web-based attack aimed at privilege escalation. |
B | VLAN hopping involves overriding a user network connection to execute malicious commands. Session hijacking involves compromising a host to elevate privileges. |
C | VLAN hopping is a brute force attack executed to gain additional access. Session hijacking involves physically disrupting a network connection. |
D | VLAN hopping involves the unauthorized transition from one VLAN to another to gain additional access. Session hijacking involves overriding a user’s web connection to execute commands. |
Question 128 |
A | Coaxial |
B | Shielded twisted pair |
C | Multimode fiber optic |
D | Unshielded twisted pair |
E | Single-mode fiber optic |
Question 129 |
A | HTTP |
B | HTML |
C | SMTP |
D | SSL |
E | FTP |
Question 130 |
A | LDAP |
B | SMTP |
C | POP |
D | IMAP |
Question 131 |
A | Latency |
B | Crosstalk |
C | Signal attenuation |
D | EMI |
Question 132 |
A | Open circuits |
B | Short circuits |
C | Split pairs |
D | Transposed wires |
Question 133 |
A | iSCSI |
B | InfiniBand |
C | CIFS |
D | Fibre Channel |
Question 134 |
A | MAC address |
B | Subnet mask |
C | IP address |
D | Default gateway |
Question 135 |
A | ntop |
B | Network Monitor |
C | Performance Monitor |
D | Event Viewer |
E | Syslog |
Question 136 |
A | ipconfig |
B | netstat |
C | tcpdump |
D | traceroute |
E | iptables |
Question 137 |
A | Site-to-site VPN |
B | Fault tolerance |
C | Remote connection |
D | Distributed server system |
E | Network management |
Question 138 |
A | Individual mode |
B | Hot backup mode |
C | High-efficiency mode |
D | Redundant mode |
E | Combined mode |
Question 139 |
A | Network map |
B | Rack diagram |
C | Wiring schematic |
D | Building blueprints |
E | Logical diagram |
Question 140 |
A | Netstat |
B | Ping |
C | Route |
D | Tracert |
E | Nslookup |
Question 141 |
A | Double NAT |
B | Bridge mode |
C | Jumbo frame |
D | DOCSIS |
E | ADSL |
Question 142 |
A | Distance |
B | Bandwidth |
C | Speed |
D | Ping time |
E | Hop count |
Question 143 |
A | Asset tracking |
B | Data security |
C | Port security |
D | Physical security |
Question 144 |
A | MTRJ |
B | RJ11 |
C | LC |
D | RJ45 |
E | F-type |
F | ST |
Question 145 |
A | SSL gateway |
B | SSL client |
C | SSL portal |
D | SSL tunnel |
Question 146 |
A | Client terminal |
B | RDP |
C | KDC |
D | Application server |
Question 147 |
A | Microwave |
B | Electrical |
C | Infrared |
D | Fiber optic |
Question 148 |
A | 110 |
B | 143 |
C | 80 |
D | 25 |
E | 989 |
Question 149 |
A | 1 unit |
B | 4 unit |
C | 2 unit |
D | 3 unit |
Question 150 |
A | RAID 1 |
B | RAID 0 |
C | RAID 5 |
D | RAID 10 |
Question 151 |
A | SONET |
B | SIP trunk |
C | Smart jack |
D | AAA server |
E | Media converter |
Question 152 |
A | RTO |
B | RPO |
C | BCP |
D | MIB |
E | RAID |
Question 153 |
A | Remove the firewall between the Internet/modem and the router. |
B | Add a firewall between the domain controller and the router. |
C | Add additional printers across both NATs. |
D | Remove one of the routers and if requires use VLANs to create separate subnets with specific firewall rules. |
Question 154 |
A | Smartcards |
B | Wireless access point |
C | Biometric systems |
D | RADIUS server |
E | Domain controller |
Question 155 |
A | SQL injection |
B | XSS |
C | Packet sniffing |
D | Directory traversal |
E | Wardriving |
Question 156 |
A | Data Link |
B | Application |
C | Network |
D | Transport |
E | Presentation |
F | Physical |
G | Session |
Question 157 |
SANUJA.COM 430 IN mx mx1.SANUJA.COM
SANUJA.COM 5 IN mx mx2.SANUJA.COM
SANUJA.COM 430 IN mx mx10.SANUJA.COM
SANUJA.COM 521 IN NS ns1.SANUJA.COM
SANUJA.COM 521 IN NS ns2.SANUJA.COM
SANUJA.COM 521 IN NS ns3.SANUJA.COM
SANUJA.COM 521 IN NS ns4.SANUJA.COM
A | NMAP –t SANUJA.COM |
B | dig –t ANY SANUJA.COM |
C | iptables –f SANUJA.COM |
D | netstat –a SANUJA.COM |
Question 158 |
A | IPSec |
B | Telnet |
C | SSL |
D | SSH |
Question 159 |
A | War driving |
B | Port scanning |
C | Port sweeping |
D | Bluejacking |
E | Brute-force |
Question 160 |
A | VLAN mismatch |
B | Corrupted config files or operating system |
C | Double NAT issue |
D | Damaged or malfunctioning fiber port |
E | Damaged or malfunctioning LAN port |
Question 161 |
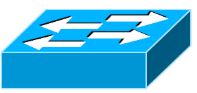
A | A switch |
B | A router |
C | A hub |
D | A gateway |
Question 162 |
A | netstat |
B | ping |
C | pathping |
D | route |
Question 163 |
A | Packet intrusion |
B | Honey pot |
C | VLAN mismatch |
D | Evil twin |
E | Rogue DHCP server |
Question 164 |
A | Store-and-forward |
B | Destination switch |
C | Source route |
D | Cut-through |
Question 165 |
A | Verify file type |
B | Verify file hash |
C | Verify file date |
D | Verify file size |
E | Verify file version |
Question 166 |
A | SaaS |
B | Hybrid |
C | PaaS |
D | Public |
E | IaaS |
F | Private |
Question 167 |
A | Temperature changes are causing attenuation in copper cabling |
B | Network wiring is run perpendicular to electrical conduit |
C | Light sensors are interfering with the network |
D | EMI from the lights is interfering with the network cables |
Question 168 |
A | WPA2 |
B | WEP |
C | WPA |
D | PEAP |
Question 169 |
A | ARP |
B | FTP |
C | SCP |
D | SIP |
Question 170 |
A | QSFP |
B | BiDi |
C | SFP |
D | GBIC |
Question 171 |
A | 8 |
B | 16 |
C | 17 |
D | 15 |
Question 172 |
A | 1 |
B | 4 |
C | 2 |
D | 3 |
E | 0 |
Question 173 |
A | SYN/ACK, SYN/ACK |
B | SYN, SYN, ACK, ACK |
C | SYN, ACK, SYN, ACK |
D | SYN, SYN/ACK, ACK |
Question 174 |
A | A privilege escalation script |
B | An SNMPv1 private community |
C | A router with default credentials |
D | An open mail relay server |
Question 175 |
A | 224.0.0.0 to 224.0.255.255 |
B | 169.254.0.0 to 169.254.255.255 |
C | 192.168.0.0 to 192.168.0.255 |
D | 10.0.0.0 to 10.0.255.255 |
Question 176 |
A | NS |
B | TXT |
C | MX |
D | AAAA |
E | A |
Question 177 |
A | Power distribution unit |
B | Power-over-Ethernet switch |
C | Powerline extender |
D | Ethernet power controller |
E | Ethernet-over-power adapter |
Question 178 |
A | NGFW |
B | RADIUS |
C | IDS |
D | NAS |
Question 179 |
A | Failover |
B | Backups |
C | Snapshots |
D | Cold sites |
Question 180 |
A | VoIP |
B | CARP |
C | SSL |
D | IPv6 |
E | QoS |
Question 181 |
A | PSH |
B | END |
C | FIN |
D | SYN |
E | URG |
Question 182 |
A | 49152 through 65535 |
B | 1 through 1024 |
C | 1024 to 49151 |
D | 1023 through 65534 |
Question 183 |
A | Single sign-on |
B | TACACS+ |
C | Local authentication |
D | LDAP |
Question 184 |
A | Password protection |
B | IP address resolution |
C | Name resolution |
D | Network switching |
Question 185 |
A | Create a new network segment with ACLs, limiting kiosks’ traffic with the internal network. |
B | Create a secondary NAT and connect the kiosks on it hence limit kiosks' ability to access the main network. |
C | Enable switchport security on the ports to which the kiosks are connected to prevent network-level attacks. |
D | Install honeypots on the network to detect and analyze potential kiosk attacks before they occur. |
E | Install an IDS to monitor all traffic to and from the kiosks. |
Question 186 |
A | There is a frequency mismatch |
B | There is a security type mismatch. |
C | There is insufficient antenna power |
D | The channel has changed |
E | The password needs to be re-entered |
Question 187 |
A | TGS |
B | Accounting |
C | Auditing |
D | Authorization |
E | Authentication |
Question 188 |
A | Fiber channel |
B | NAS |
C | SAN |
D | FTP |
E | Jumbo frames |
Question 189 |
A | PSK |
B | CCMP-AES |
C | WEP |
D | EAP-PEAP |
Question 190 |
A | Network firewall |
B | Demarcation point |
C | Demarcation point |
D | Wireless controller |
E | Wireless endpoint |
Question 191 |
A | Somewhere you are |
B | Something you know |
C | Something you do |
D | Something you have |
Question 192 |
A | Security |
B | Application |
C | Setup |
D | System |
Question 193 |
A | Setup |
B | Application |
C | Security |
D | System |
Question 194 |
A | RDP |
B | PBX |
C | MTBF |
D | MDF |
E | IDF |
Question 195 |
A | There is less local congestion on the wireless network |
B | The firewall is configured to throttle traffic to specific websites |
C | The wireless access points were misconfigured |
D | The testing server for the wired network was farther away |
Question 196 |
A | Hand geometry |
B | Tamper detection |
C | Biometrics |
D | Single sign-on (SSO) |
E | Pattern recognition |
Question 197 |
A | Periodically view the server logs |
B | Use port mirroring |
C | Use SQL injectors |
D | Install an inline tap |
E | Configure port aggregation |
Question 198 |
A | Application |
B | Presentation |
C | Session |
D | Physical |
E | Transport |
F | Network |
G | Data link |
Question 199 |
A | PPTP |
B | IPsec |
C | FTPS |
D | L2TP |
Question 200 |
A | Loss of full control over data resources |
B | Increased malware exposure |
C | Decreased performance of the internal network |
D | Inconsistent data accessability |
E | Incompatibility with the current network |
← |
List |
→ |
| 1 | 2 | 3 | 4 | 5 |
| 6 | 7 | 8 | 9 | 10 |
| 11 | 12 | 13 | 14 | 15 |
| 16 | 17 | 18 | 19 | 20 |
| 21 | 22 | 23 | 24 | 25 |
| 26 | 27 | 28 | 29 | 30 |
| 31 | 32 | 33 | 34 | 35 |
| 36 | 37 | 38 | 39 | 40 |
| 41 | 42 | 43 | 44 | 45 |
| 46 | 47 | 48 | 49 | 50 |
| 51 | 52 | 53 | 54 | 55 |
| 56 | 57 | 58 | 59 | 60 |
| 61 | 62 | 63 | 64 | 65 |
| 66 | 67 | 68 | 69 | 70 |
| 71 | 72 | 73 | 74 | 75 |
| 76 | 77 | 78 | 79 | 80 |
| 81 | 82 | 83 | 84 | 85 |
| 86 | 87 | 88 | 89 | 90 |
| 91 | 92 | 93 | 94 | 95 |
| 96 | 97 | 98 | 99 | 100 |
| 101 | 102 | 103 | 104 | 105 |
| 106 | 107 | 108 | 109 | 110 |
| 111 | 112 | 113 | 114 | 115 |
| 116 | 117 | 118 | 119 | 120 |
| 121 | 122 | 123 | 124 | 125 |
| 126 | 127 | 128 | 129 | 130 |
| 131 | 132 | 133 | 134 | 135 |
| 136 | 137 | 138 | 139 | 140 |
| 141 | 142 | 143 | 144 | 145 |
| 146 | 147 | 148 | 149 | 150 |
| 151 | 152 | 153 | 154 | 155 |
| 156 | 157 | 158 | 159 | 160 |
| 161 | 162 | 163 | 164 | 165 |
| 166 | 167 | 168 | 169 | 170 |
| 171 | 172 | 173 | 174 | 175 |
| 176 | 177 | 178 | 179 | 180 |
| 181 | 182 | 183 | 184 | 185 |
| 186 | 187 | 188 | 189 | 190 |
| 191 | 192 | 193 | 194 | 195 |
| 196 | 197 | 198 | 199 | 200 |
| End |
Based on general knowledge and CompTIA guidelines published in 2020.
FAQ | Report an Error
Study outline at: CompTIA Exams Guide
Disclaimer: While every reasonable effort is made to ensure that the information provided is accurate, no guarantees for the currency or accuracy of information are made. It takes several proof readings and rewrites to bring the quiz to an exceptional level. If you find an error, please contact me as soon as possible. Please indicate the question ID-Number or description because server may randomize the questions and answers.